
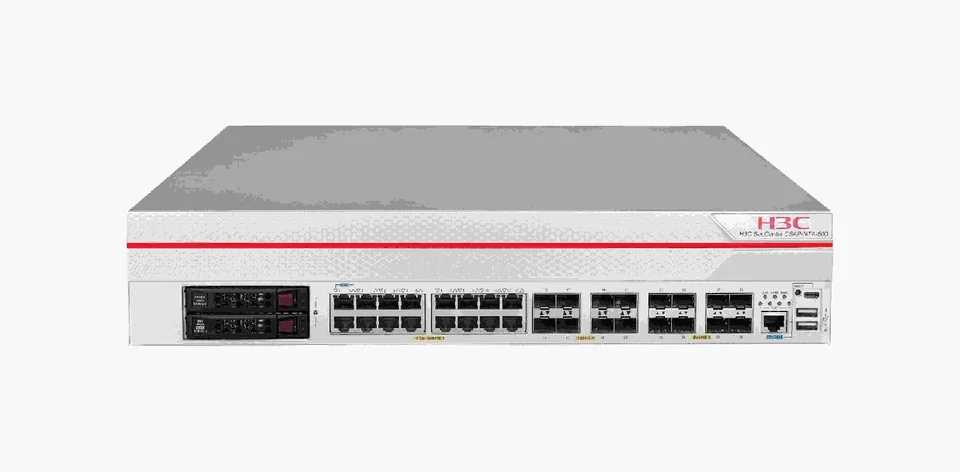
H3C NS-SecCenter CSAP-NTA-500+LIS Sec Center CSAP-NTA-500 Network Traffic Threat Detection Probe Bundle, includes 1 CSAP-NTA-500 host and a one-year signature database upgrade license
Marca H3C
N/AVerificado
H3C NS-SecCenter CSAP-NTA-500+LIS
Modelo (MPN)
NS-SecCenter CSAP-NTA-500+LIS
Condición
Sellado de fábrica
Agotado
H3C NS-SecCenter CSAP-NTA-500+LIS Sec Center CSAP-NTA-500 Network Traffic Threat Detection Probe Bundle, includes 1 CSAP-NTA-500 host and a one-year signature database upgrade license. Traffic Collection: Supports the collection of IPv4, IPv6, and VXLAN traffic and protocol parsing.. Weak Password Detection: Supports weak password detection for Telnet, FTP, POP3, SMTP, and IMAP protocols.. Threat Intelligence Detecti
Especificaciones clave
DescriptionH3C Sec Center CSAP-NTA-500 Network Traffic Threat Detection Probe Bundle, includes 1 CSAP-NTA-500 host and a one-year signature database upgrade license
Traffic CollectionSupports the collection of IPv4, IPv6, and VXLAN traffic and protocol parsing.
Weak Password DetectionSupports weak password detection for Telnet, FTP, POP3, SMTP, and IMAP protocols.
Virus DetectionThe system supports detection engines based on both a built-in virus detection engine and the YARA rule database to identify malicious code such as known vulnerabilities, Trojans, worms, viruses, and hacking tools.
Threat Intelligence DetectionSupports local detection of malicious IPs, URLs, domain names, MD5 hashes, and more
Machine learning detectionSupports the use of machine learning models to detect webshell files, malicious PE files, and DGA domains.
Tu precio
Mejor precio
$19,862.80
Precio de lista: $248,285.00Ahorra 92%
Disponibilidad Agotado
Cantidad
¿Necesita ayuda con la configuración?
Nuestros ingenieros certificados CCIE pueden ayudarle a verificar la compatibilidad.
Pago seguro
VISA
Pay
WIRE
Envío rápido
Red logística global orientada a la entrega el mismo día.
48hrs
Envío medio
99%
A tiempo
Calidad garantizada
Cada unidad supera una inspección rigurosa de 38 puntos.
3Year
Garantía
0.1%
Tasa RMA
Alcance global
Empresas de 6 continentes confían en nosotros.
85+
Países
20k+
Clientes
Soporte experto
Ingenieros de red certificados listos para ayudar con la configuración.
24/7
Asistencia
CCIE
Certificado
Resumen
Especificaciones
| Catalog Description | |
|---|---|
| Description | H3C Sec Center CSAP-NTA-500 Network Traffic Threat Detection Probe Bundle, includes 1 CSAP-NTA-500 host and a one-year signature database upgrade license |
| Key Specifications | |
| Traffic Collection | Supports the collection of IPv4, IPv6, and VXLAN traffic and protocol parsing. |
| Weak Password Detection | Supports weak password detection for Telnet, FTP, POP3, SMTP, and IMAP protocols. |
| Virus Detection | The system supports detection engines based on both a built-in virus detection engine and the YARA rule database to identify malicious code such as known vulnerabilities, Trojans, worms, viruses, and hacking tools. |
| Threat Intelligence Detection | Supports local detection of malicious IPs, URLs, domain names, MD5 hashes, and more |
| Machine learning detection | Supports the use of machine learning models to detect webshell files, malicious PE files, and DGA domains. |
| Dynamic sandbox detection | Uses dynamic behavioral analysis technology in a sandbox to detect known and unknown threats; the sandbox detection environment supports Windows 10 x64, Windows XP, Windows 7 x86, and CentOS operating systems |
| Product Specifications | |
| Traffic Collection | Supports the collection of IPv4, IPv6, and VXLAN traffic and protocol parsing. |
| File Recovery | Supports recovering files in specified formats from HTTP, FTP, POP3, SMTP, IMAP, and SMB/CIFS protocols. File categories include documents, executables, scripts, compressed files, text, images, multimedia, and software data. |
| File Format Detection | Supported formats include Office (Word, Excel, PPT, RTF), PDF, HTML, JS, PE (EXE, DLL, ELF, etc.), SWF, compressed archives (ZIP, 7Z, RAR, CAB, GZIP, TAR, etc.), and script files (BAT, VBS, SH, PY, Power Shell), among others. |
| Intrusion Detection | Supports detection of common network threat events, including botnets, worms, Trojans, injection attacks, cross-site scripting (XSS) attacks, Web Shells, other Web attacks, cyber weapons, vulnerability exploits, exploits targeting OA system applications, attacks exploiting known vulnerabilities in Web servers and plugins, and penetration testing components. |
| Weak Password Detection | Supports weak password detection for Telnet, FTP, POP3, SMTP, and IMAP protocols. |
| Virus Detection | The system supports detection engines based on both a built-in virus detection engine and the YARA rule database to identify malicious code such as known vulnerabilities, Trojans, worms, viruses, and hacking tools. |
| Threat Intelligence Detection | Supports local detection of malicious IPs, URLs, domain names, MD5 hashes, and more |
| Machine learning detection | Supports the use of machine learning models to detect webshell files, malicious PE files, and DGA domains. |
| Dynamic sandbox detection | Uses dynamic behavioral analysis technology in a sandbox to detect known and unknown threats; the sandbox detection environment supports Windows 10 x64, Windows XP, Windows 7 x86, and CentOS operating systems |
| Network Behavior Simulation | Supports simulation of various common network protocols, including ICMP, DNS, HTTP, SMTP, POP3, and more. It simulates responses from external servers to samples, enabling the collection of additional network behavior data from malicious samples without connecting to the external network. |
| Adaptive Sandbox Count | Based on the length of the file detection queues in each sandbox, the system can automatically adjust the number of sandboxes to dynamically adapt to changing network traffic patterns and different application scenarios; |
| On-sample embedded file detection | Can open and run the embedded files in the sample, and perform threat determination based on the line is |
| Nested Compressed File Detection | Supports threat detection for subfiles within multi-level (at least 3 levels) nested compressed files. |
| Digital signature detection | Can analyze digital signature status information of samples, including certificate verification results, timestamps, serial numbers, users, validity periods, etc., and can identify signature validity. It can identify information such as expired certificates and forgeries. |
| Multi-sample parallel detection | Sandbox supports concurrent execution of multiple x samples, and isolates the line is logs of different samples to improve detection performance |
| Custom Rule Detection | Supports custom detection rules, which can be added manually or imported in bulk. Custom detection can be configured using various keywords, including protocol types, threat classifications, traffic direction, MITRE ATT&CK, and NSA/CSS. |
| Sampling of Network Behavior | When manually uploaded samples are executed in the sandbox, their network behavior can be captured, saved as a PCAP file, and downloaded for local analysis. |
| File masquerade identification | Can identify formats based on file content instead of file extensions. |
| Event Analysis and Viewing | Provides the ability to view detailed information about threat events, including event descriptions, transmission details (source and destination IP addresses, source and destination ports, protocol types), geographic location, and threat detection results. This information can be viewed via a web page or exported as a file. |
| Traffic storage | Supported store threat traffic discovered by the traffic detection module |
| Security Analysis | Supports online viewing of comprehensive analysis reports, uploading of local suspicious files for detection, and automatic downloading and scanning of network-shared files from specified URLs. |
| Ordering Information | |
| SFPGigabit Optical Port | |
| 02312170 | SFP-GE-LH40-SM1310 - Optical Module - SFP-GE - Single-Mode Module (1310 nm, 40 km, LC) |
| 02312172 | SFP-GE-LH40-SM1550 - Optical Module—SFP—GE—Single-Mode Module—(1550 nm, 40 km, LC) |
| 02312173 | SFP-GE-LH80-SM1550 - Optical Module - SFP-GE - Single-Mode Module - (1550 nm, 80 km, LC) |
| 0231A085 | SFP-GE-T - SFP GEElectrical Port Module(100m,RJ45) |
| 0231A562 | SFP-GE-SX-MM850-A - Optical Module - SFP-GE - Multimode Module (850 nm, 0.55 km, LC) |
| 0231A563 | SFP-GE-LX-SM1310-A - Optical Module - SFP-GE - Single-Mode Module (1310 nm, 10 km, LC) |
| 0231A960 | SFP-GE-T-D - SFP GEElectrical Port Module(100m,RJ45) |
| 0231A961 | SFP-GE-SX-MM850-D - Optical Module - SFP-GE - Multimode Module (850 nm, 0.55 km, LC) |
| 0231A962 | SFP-GE-LX-SM1310-D - Optical Module - SFP-GE - Single-Mode Module (1310 nm, 10 km, LC) |
| 0231A963 | SFP-GE-LH40-SM1310-D - Optical Module - SFP-GE - Single-Mode Module (1310 nm, 40 km, LC) |
| 0231A964 | SFP-GE-LH80-SM1550-D - Optical Module - SFP-GE - Single-Mode Module - (1550 nm, 80 km, LC) |
| SFP/SFP+10GOptical Port | |
| 0231A0A6 | SFP-XG-SX-MM850-A - SFP+ 10GModule(850nm,300m,LC) |
| 0231A0A8 | SFP-XG-LX-SM1310 - SFP+ 10GModule(1310nm,10km,LC) |
| 0231A0SP | SFP-XG-LH40-SM1550 - SFP+ 10GModule(1550nm,40km,LC) |
| 0231A1RP | SFP-XG-SX-MM850-D - SFP+ 10GModule(850nm,300m,LC) |
| 0231A1RQ | SFP-XG-LX-SM1310-D - SFP+ 10GModule(1310nm,10km,LC) |
| 0231A1RR | SFP-XG-LH40-SM1550-D - SFP+ 10GModule(1550nm,40km,LC) |
| 0231A2L3 | SFP-XG-LX-SM1310-E - SFP+ 10GModule(1310nm,10km,LC) |
| 0231A2L4 | SFP-XG-SX-MM850-E - SFP+ 10GModule(850nm,300m,LC) |
| SATAHard Drive | |
| 0231A2WY | 0231A2WY - H3C CSAP Probe Appliance |
| 0231A4PX | NS-HDD-1T-SATA-SFF - H3C Sec Path Series,1TB 2.5inch SATA HDD Hard Drive Module |
| 0231A4PY | NS-SSD-480G-SATA-SFF - H3C Sec Path Series,480GB 2.5inch SATA SSD Hard Drive Module |
| Insert Card | |
| 0231A4YN | NSQM1GP4FBA - H3C Sec Path F1000Series,4-PortSFPInterface Module |
| SFP Gigabit Port | |
| 0231AB2G | NS-NIM-TG6A - H3C Sec Path F1000Series6-Port10GEthernetoptical interface Module(SFP+) |
| SFP+ 10G Port | |
| Power Supply | |
| 0231A6NA | PSR450-12AHD - 450W High-Voltage DC power Module (Supports AC/336V High-Voltage DC, with air exhaust on the front panel) |
| 0231A6NB | PSR450-12D - 450W DC power Module (Power Supply panel-side airflow exhaust) |
| 0231A8FP | PSR250-12A1 - 250W AC power Module (Power Supply panel-side airflow exhaust) |
| functions feature license certificate | |
| 3130A510 | LIS-SecCenter CSAP-NTA-V3-1Y - H3C Sec Center CSAP-NTA-V3 Signature Database Upgrade License, 1 year |
| Product Identity | |
| Brand | H3C |
| Series | H3C Sec Center CSAP Full-Traffic Threat Probe Product |
Reseñas
Aún no hay reseñas
Sé el primero en calificar este producto.
Garantía
Política de Garantía Estándar
Todo el hardware vendido por ITMall incluye 3 años de mantenimiento gratuito y 1 año de sustitución RMA. Consulte nuestra Política de garantía para más detalles.
- Sustitución anticipada de 1 año (RMA)
- Servicio de reparación gratuito durante 3 años
- Cobertura completa de defectos funcionales
Proceso de RMA sin complicaciones
Hemos simplificado las devoluciones para reducir el tiempo de inactividad e incluimos diagnóstico previo por nuestros ingenieros.
- Plazo de devolución de 30 días
- Portal RMA automatizado con seguimiento inmediato
- Sin tarifa de reposición por problemas funcionales
Soporte técnico certificado
Ingenieros CCIE ofrecen orientación sobre compatibilidad, configuración y diagnóstico sin coste adicional.
- Consulta de topología gratuita antes de la venta
- Diagnóstico remoto y asesoramiento de firmware
- Pruebas de laboratorio antes del envío
Logística Global y Embalaje
Enviamos a más de 85 países con embalaje antiestático premium. Los pedidos antes de las 14:00 (GMT+8) suelen salir el mismo día.
- Cajas de doble pared con espuma a medida
- Envío neutro para socios de canal
- Seguimiento en tiempo real con FedEx / DHL / UPS
Recursos
No hay descargas disponibles para este producto.
Preguntas frecuentes
¿Este producto es nuevo?
Sí. Salvo que figure como reacondicionado, todos los productos están sellados de fábrica y proceden de canales autorizados.
¿Cuál es el periodo de garantía?
Ofrecemos una garantía integral de 3 años para defectos de hardware y sustitución anticipada.
¿Ofrecen descuentos por volumen?
Sí. Solicite una cotización personalizada para pedidos grandes o proyectos.
¿Con qué rapidez pueden enviar?
Los artículos en stock pedidos antes de las 15:00 EST salen el mismo día, con opciones de uno o dos días.
¿Todavía tienes preguntas?